TryZ
I work on web and application security — penetration testing, finding the places where an app trusts a little too much, and writing up how to close them.
Most of my time goes into recon, auth flows and APIs. When the tool I need doesn't exist, I build it.
real name
          .                                                      .
        .n                   .                 .                  n.
  .   .dP                  dP                   9b                 9b.    .
 4    qXb         .       dX                     Xb       .        dXp     t
dX.    9Xb      .dXb    __                         __    dXb.     dXP     .Xb
9XXb._       _.dXXXXb dXXXXbo.                 .odXXXXb dXXXXb._       _.dXXP
 9XXXXXXXXXXXXXXXXXXXVXXXXXXXXOo.           .oOXXXXXXXXVXXXXXXXXXXXXXXXXXXXP
  `9XXXXXXXXXXXXXXXXXXXXX'~   ~`OOO8b   d8OOO'~   ~`XXXXXXXXXXXXXXXXXXXXXP'
    `9XXXXXXXXXXXP' `9XX'   [!]    `98v8P'    [!]   `XXP' `9XXXXXXXXXXXP'
        ~~~~~~~       9X.          .db|db.          .XP       ~~~~~~~
          |             )b.  .dbo.dP'`v'`9b.odb.  .dX(             |
          |           ,dXXXXXXXXXXXb     dXXXXXXXXXXXb.            |
          +---[0x0]--dXXXXXXXXXXXP'   .   `9XXXXXXXXXXXb--[0xF]----+
                    dXXXXXXXXXXXXb   d|b   dXXXXXXXXXXXXb
                    9XXb'   `XXXXXb.dX|Xb.dXXXXX'   `dXXP
                     `'      9XXXXXX(   )XXXXXXP      `'
                              XXXX X.`v'.X XXXX
                              XP^X'`b   d'`X^XX
                              X. 9  `   '  P )X
                              `b  \  | |  /  d'
                               |   | | | |   |
                               |   | | | |   |
                               '   | | | |   '
                                   ' ' ' '
selected work
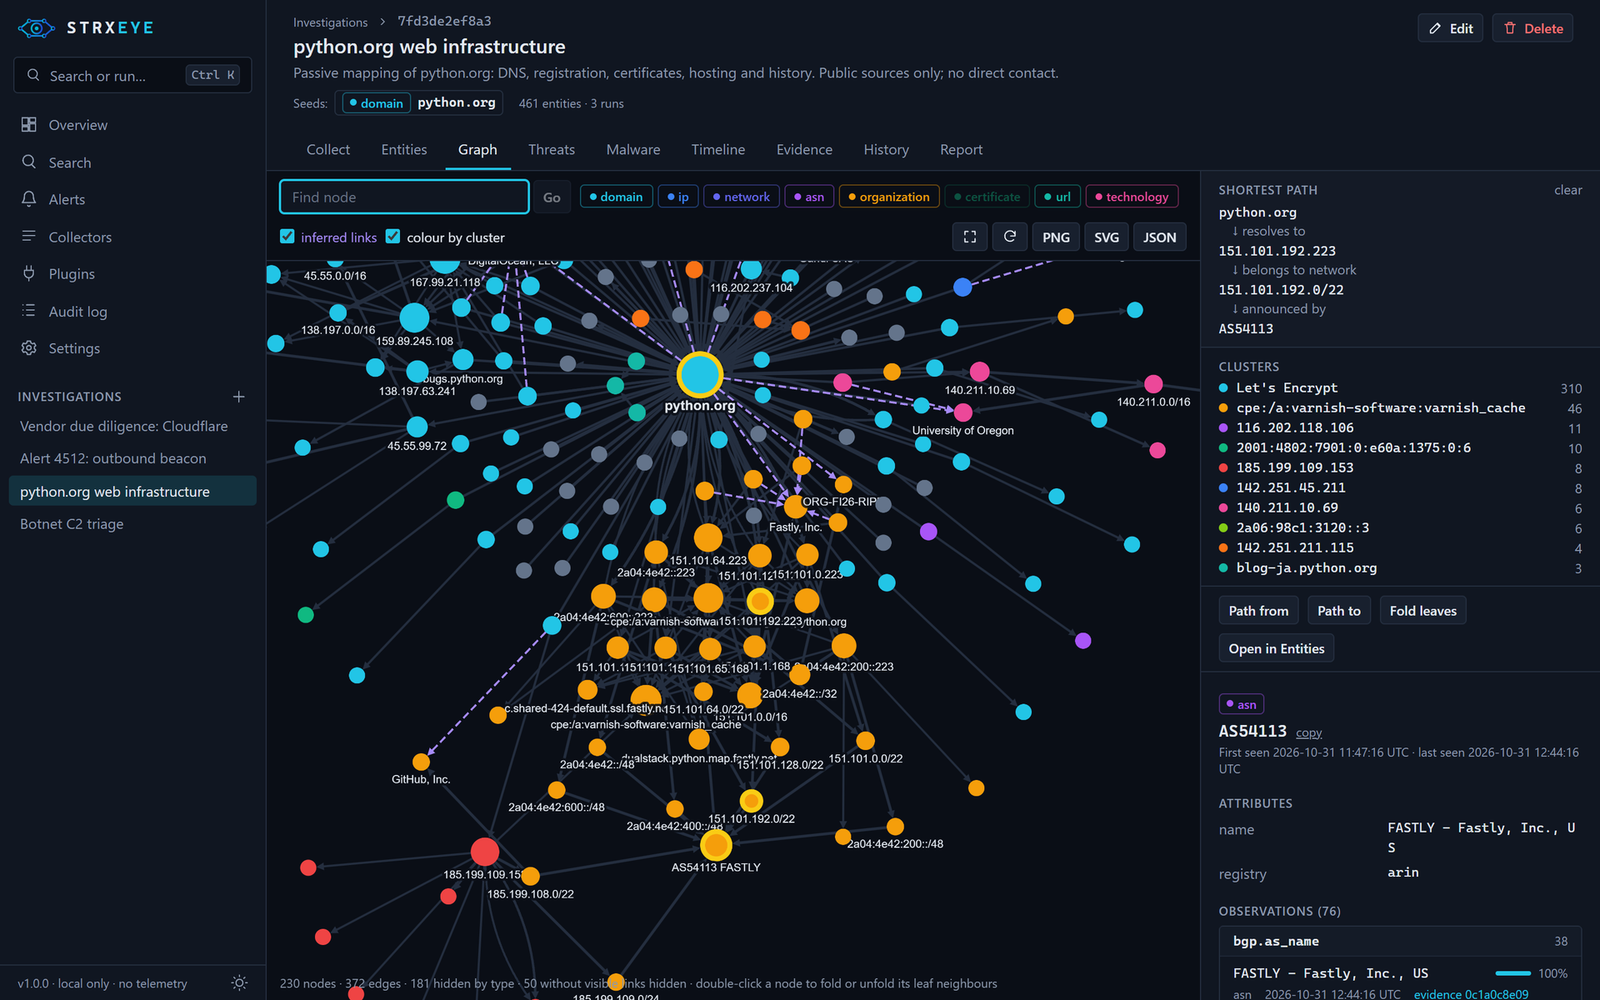
A local-first OSINT & threat-intel workbench.
Give it a domain, an IP, an AS number, a hash or a company. It asks dozens of public sources — DNS, RDAP, certificate logs, BGP, block lists, OTX, abuse.ch, Malpedia — and pulls the answers into one graph you can walk through.
Every fact keeps its source, its timestamp and the raw response. Nothing touches the target unless you say so.
- exports
- HTML, JSON, CSV, STIX 2.1
- runs on
- Windows, Linux, macOS
- stack
- Python, React
- license
- MIT
coming soon
Something new is on the bench.
I'm working on a new program. No name yet, no date yet — it lands on GitHub when it's ready, not before.
| building
code, releases, and the occasional half-finished idea.